About
About Me
I am a certified Cloud and Network Engineer with experience designing, implementing, and supporting secure AWS cloud, hybrid connectivity, Kubernetes/EKS, Terraform automation, and enterprise network infrastructure. My background combines deep network engineering experience with recent hands-on cloud migration, monitoring, security, and infrastructure automation work.
Highlights
- Certified CCIE, AWS Solutions Architect, CKA, Terraform Associate, ITIL 4, and Cisco SD-WAN Specialist
- Eligible to work for any employer in New Zealand
- Senior Cloud and Network Engineer with 17+ years of IT infrastructure experience
- Strong hands-on experience in AWS, Kubernetes/EKS, Terraform, GitLab CI/CD, and hybrid cloud networking
Skills
Core Skills
Experience
Experience Timeline
Senior Infrastructure Engineer (Network & Cloud)
- Design, deploy, and maintain secure AWS cloud infrastructure across UAT and production environments using VPC, EC2, S3, IAM, CloudWatch, Route 53, CloudFront, API Gateway, and load balancing services.
- Build and maintain Infrastructure as Code using Terraform, including reusable modules for VPC, subnets, route tables, security groups, NACLs, EC2, EKS, ECS, ALB/NLB, RDS, and S3.
- Implement GitLab CI/CD pipelines to automate infrastructure provisioning and application deployment, improving deployment consistency and reducing manual effort.
- Configure hybrid connectivity and cloud networking using Site-to-Site VPN, AWS Transit Gateway, subnets, NAT Gateways, routing, and firewall policies.
- Support cloud security, monitoring, disaster recovery, patching, documentation, and operational troubleshooting across UAT and production environments.
Assistant Manager (Team Leader) / System Engineer
- Led engineers responsible for enterprise network implementation, technical support, project delivery, and service operations
- Designed and implemented enterprise network, data centre, routing, LAN, firewall, wireless, server, storage, and structured cabling solutions.
- Prepared BOMs, proposals, WBS, HLD/LLD, topology diagrams, project documentation, and managed customer/vendor escalations
Network Administrator
- Administered network, server, desktop, Active Directory, user support and infrastructure operations across school/business IT environments.
System and Network Engineer
- Implemented network, server, Active Directory, mail, DNS, DHCP, VPN, wireless and structured cabling solutions for customer projects.
Education
Academic Background
Bachelor of Computer Science (B.C.Sc)
Credentials
Certifications
CCIE Enterprise Infrastructure
Issued by: Cisco
- Expert-level enterprise networking certification
- Strong routing, switching, network design, and troubleshooting skills
- Validates advanced network engineering capability
Certified Kubernetes Administrator
Issued by: The Linux Foundation
- Hands-on Kubernetes cluster administration skills
- Experience with workloads, services, networking, storage, and troubleshooting
- Supports EKS and containerized infrastructure operations
AWS Solutions Architect – Associate
Issued by: Amazon Web Services
- Skilled in designing secure and scalable AWS architectures
- Experience with VPC, EC2, IAM, Route 53, load balancing, and high availability
- Supports cloud migration and infrastructure design projects
HashiCorp Certified: Terraform Associate (003)
Issued by: HashiCorp
- Infrastructure as Code experience using Terraform
- Skilled in reusable modules, state management, and cloud provisioning
- Supports automated and repeatable AWS infrastructure deployment
AWS Certified Cloud Practitioner
Issued by: Amazon Web Services
- Foundational understanding of AWS cloud services, architecture, security, and pricing
- Knowledge of core AWS services including EC2, S3, IAM, VPC, CloudWatch, and billing concepts
- Supports cloud adoption, infrastructure operations, and AWS solution discussions
Cisco Certified Specialist - Enterprise SD-WAN
Issued by: Cisco
- Specialized knowledge in Cisco SD-WAN architecture and solutions
- Skills in SD-WAN deployment, configuration, troubleshooting, and operations
- Supports enterprise WAN transformation, secure connectivity, and cloud access
Portfolio
Featured Projects
Cloud / Kubernetes Project
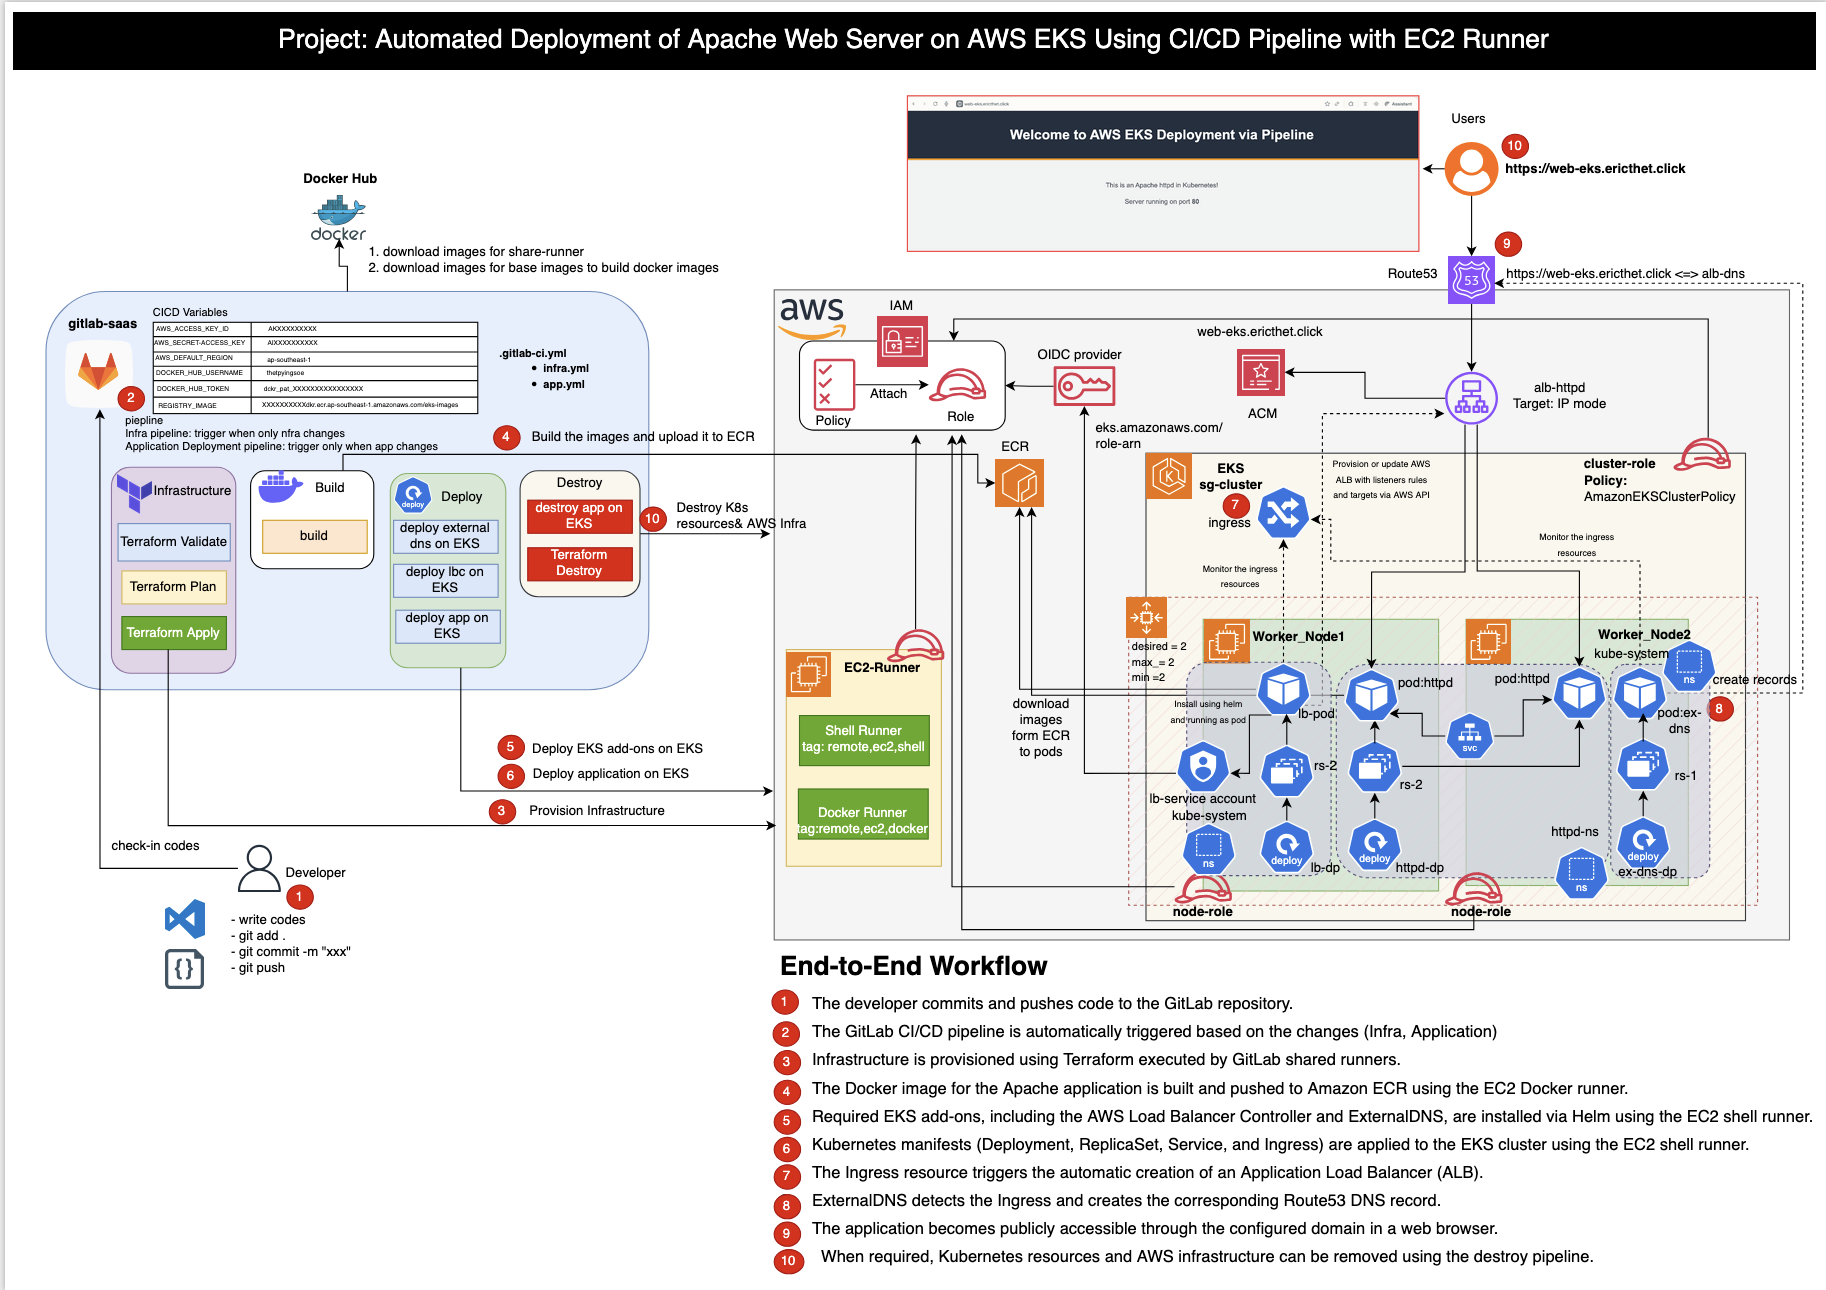
Apache Web Application Deployment on AWS EKS with GitLab CI/CD
Deployed an Apache web application on Amazon EKS using Kubernetes, AWS Load Balancer Controller, ExternalDNS, ACM, Route 53, and GitLab CI/CD. This project demonstrates automated cloud-native application delivery on AWS.
- Provisioned AWS infrastructure and EKS components for application hosting
- Used Kubernetes Deployment, Service, and Ingress for application exposure
- Integrated ALB Ingress, ACM certificate, Route 53 DNS, and ExternalDNS
- Automated build and deployment workflow using GitLab CI/CD
Cloud Logging / Security Monitoring Project
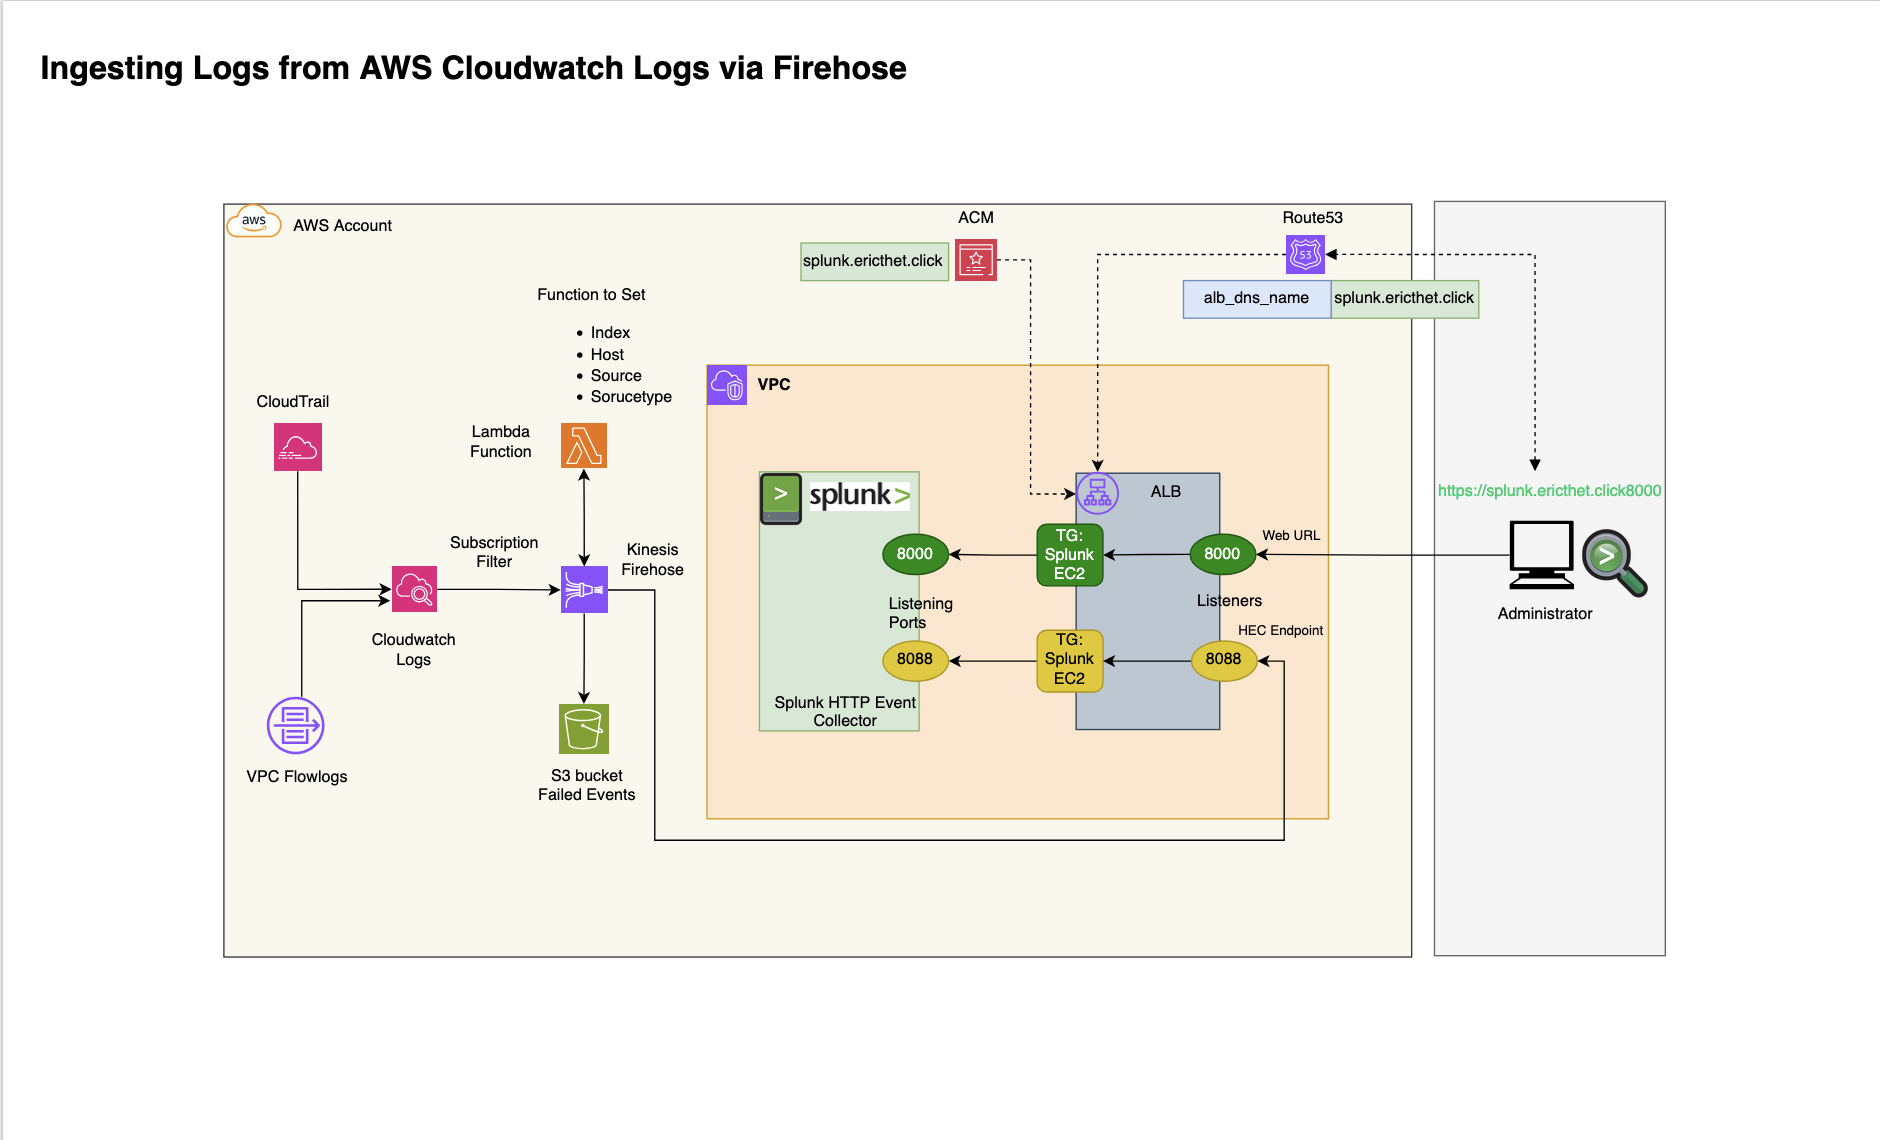
Ingesting AWS Logs into Splunk via Kinesis Firehose
Built a log ingestion pipeline to stream AWS logs into Splunk using Amazon Kinesis Data Firehose. This project demonstrates centralized log forwarding, cloud monitoring, and security visibility for AWS workloads.
- Configured AWS log ingestion workflow using Kinesis Data Firehose to forward logs into Splunk
- Supported centralized monitoring and security analysis by sending AWS service logs to a SIEM platform
- Demonstrated cloud logging architecture for operational visibility, troubleshooting, and compliance monitoring
- Integrated AWS-native log delivery with Splunk dashboards and search capability
Cloud Security / Private Connectivity Project
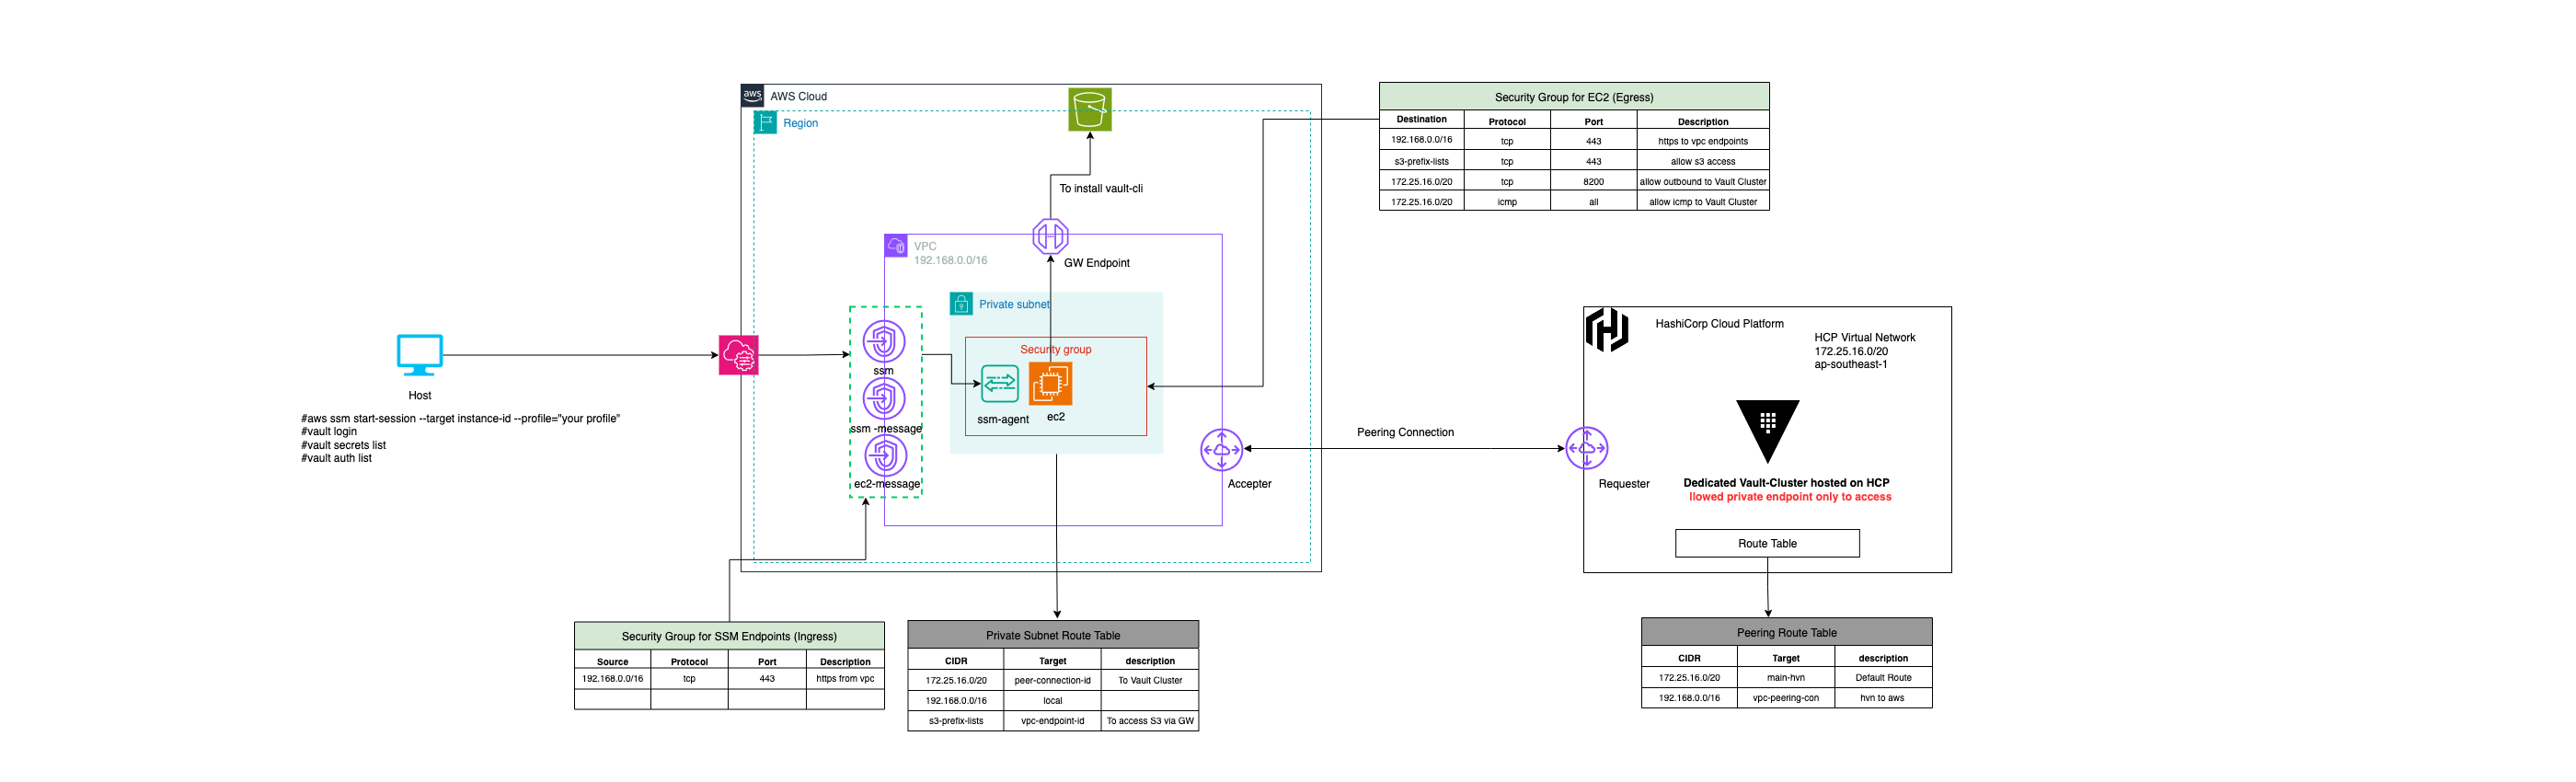
Private HCP Vault Deployment with AWS VPC Peering Integration
Deployed a private HashiCorp Cloud Platform Vault cluster and integrated it with AWS using VPC peering. This project demonstrates secure private connectivity from an EC2 private instance to HCP Vault without public access.
- Provisioned HCP Vault Dedicated and AWS infrastructure using Terraform
- Established private VPC peering between AWS VPC and HashiCorp Virtual Network
- Configured route tables and security groups for secure private Vault access
- Verified Vault CLI connectivity from a private EC2 instance using SSM Session Manager
Cloud Automation / Cost Optimisation Project
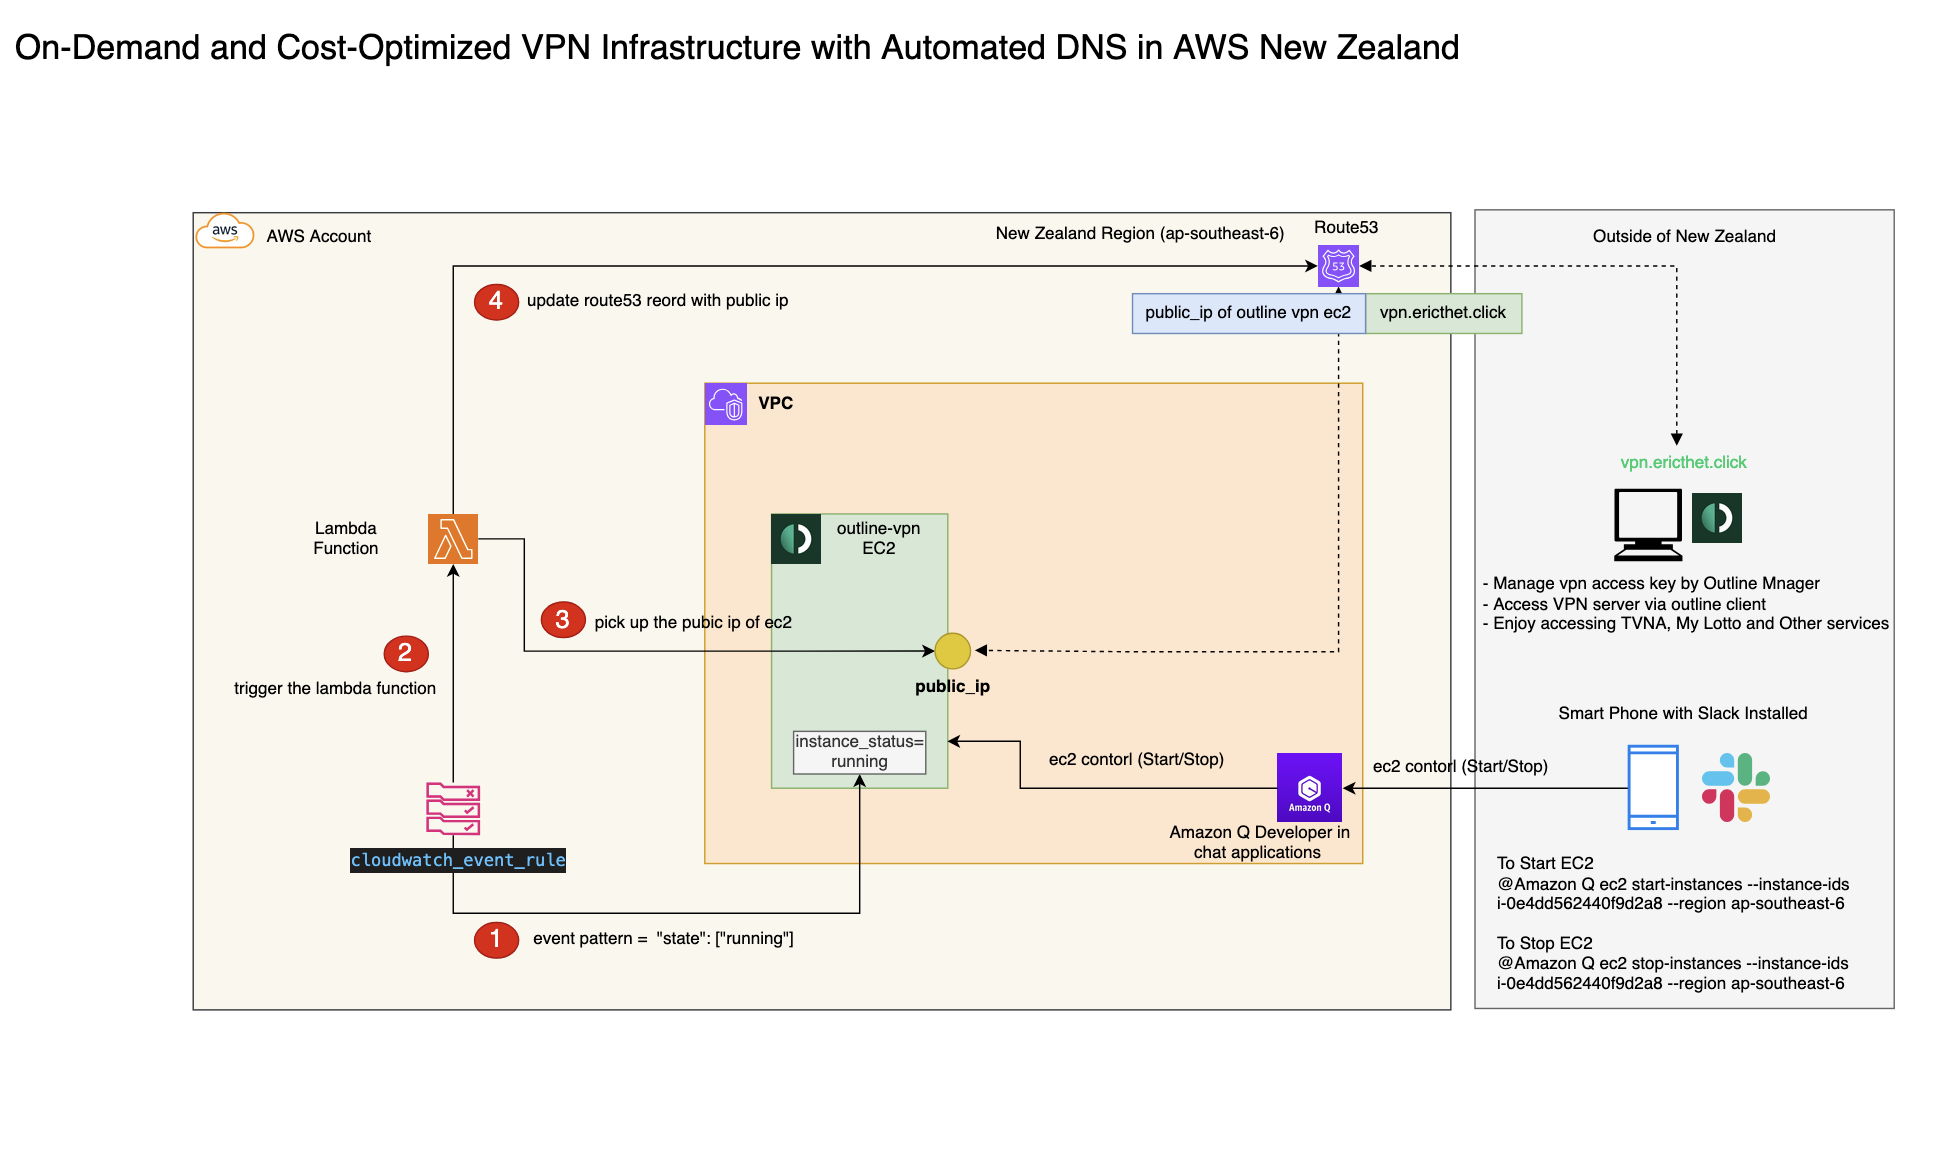
On-Demand and Cost-Optimized VPN Infrastructure with Automated DNS in AWS New Zealand
Built an on-demand VPN infrastructure in the AWS Auckland region using Terraform, EC2, Lambda, EventBridge, Route 53, and Amazon Q Slack integration. The solution allows the VPN server to be started and stopped through Slack commands, while automatically updating DNS records when the EC2 public IP changes.
- Provisioned an Outline VPN server on Amazon EC2 using Terraform
- Used Amazon Q in Slack to remotely start and stop the VPN instance
- Triggered Lambda with EventBridge when the EC2 instance enters running state
- Automated Route 53 DNS updates for the latest EC2 public IP address
- Reduced estimated monthly cost by using an on-demand server model
Contact
Get In Touch
Contact Details
Email: mgthetpinesoe@gmail.com
Phone: +65 86205028
Location: Singapore | Open to relocate to New Zealand
Work rights: Open work visa holder — eligible to work for any employer in New Zealand until April 2029
What I’m Interested In
I am interested in cloud infrastructure, platform engineering, and secure hybrid connectivity. My focus areas include AWS cloud operations, Kubernetes/EKS, Terraform automation, CI/CD-driven deployments, VPN, Transit Gateway, routing, monitoring, backup, compliance remediation, and building reliable high-availability systems for production environments.